Techseya is now techseya (Pvt) Ltd
Safeguarding customer trust for two years ,we have registered Techseya (Pvt) Ltd under Companies Act No.7 of 2007 on 17/01/2022.
Try Amazing Techseya AI Services
Try Amazing Techseya AI Services

Safeguarding customer trust for two years ,we have registered Techseya (Pvt) Ltd under Companies Act No.7 of 2007 on 17/01/2022.
Dear customer, Techseya has provided high quality service to you for two years, and Techseya is committed to providing you high quality service in the future. We are always committed to provide superior customer service to our customers and because you are very valuable to us, we strive to provide our customer service in a…

Techseya is a trusted software company in Sri Lanka, specializing in app development, web development, and software solutions. We follow a structured and transparent process when starting a new project to ensure efficiency and client satisfaction. Our Project Development Process 1. Initial Discussion & Requirement Gathering 2. Creating the Software Requirement Specification (SRS) 3. Project…
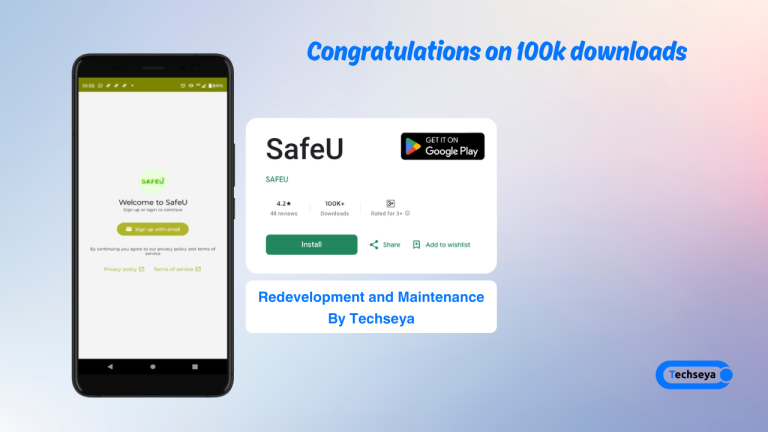
SafeU mobile application has successfully reached a 100,000 downloads count on the Google Play Store, an achievement appreciated and that underscores the increasing popularity and attention of SafeU application amongst its users. Not only is this success a result of that application’s ability to improve child safety, but also the commitment and knowledge of Techseya,…
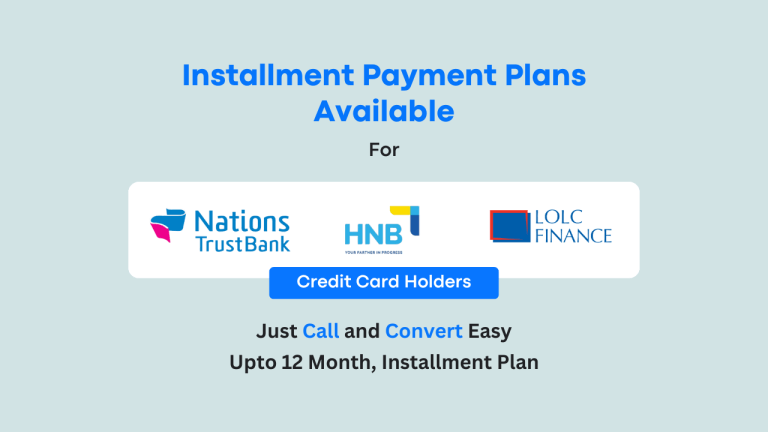
Eligibility Criteria for Credit Card Payments Project Value: Projects or services valued above LKR 80,000 are eligible for credit card payments. Client Type: Service Eligibility: Applies to all Techseya services, including: Installment Plans: Credit Card Requirements: Approval Process: Refund Policy: Payment Terms:
techseya We started Apps, Software manufacturing as a business. Many of our apps are currently available in the Google Play Store and Amazon App Store. Our Techseya Team always strives to provide a very reliable and friendly service. Get the best quality service from us that suits your needs

A serious vulnerability in React Server Components (CVE-2025-55182) has been disclosed responsibly. This issue affects React 19 and major frameworks built on it, including Next.js, which is tracked as CVE-2025-66478. The vulnerability has a CVSS score of 10.0, meaning it allows attackers to possibly influence server-side execution and, under certain conditions, achieve remote code execution…